The Locked Screen and the Legal Clock: A Partner's First Morning After a Cyber Breach
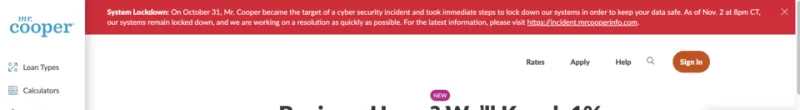
Photo: Eric n dfw, CC BY-SA 4.0, via Wikimedia Commons
The document management system will not open. A colleague forwards a client email that looks almost right — same letterhead, slightly wrong domain. On the screen, a text file names a sum and a deadline. For a professional firm, the first instinct is often to fix the problem quietly before anyone outside the partnership hears about it. That instinct is understandable and frequently counterproductive.
A cyber incident is not only a technology event. It is a client-confidentiality event, a regulatory event and, depending on the policy wording, an insurance event. The first 48 hours are less about heroics than about sequence: who decides, who records, who calls, and what the firm says before speculation does the rounds.
Contain, but do not wipe the scene
The opening move is to stop the spread without destroying the evidence that insurers, forensic investigators and regulators will need. Disconnect affected machines from the network — physically if necessary — but resist the urge to power down, rebuild or run a clean-up tool across the estate. Volatile evidence such as running processes and memory can disappear on shutdown. A photograph of the ransom note, with the time and the machine identified, is worth more than a hurried reboot.
One partner should take control of the incident log: a running, time-stamped record of what was seen, what was done, who was called and what was decided. It need not be elegant. It must be contemporaneous. In the days that follow, this log will support the insurer notification, the regulatory assessment and any later client explanation.
The calls that cannot wait
Before midday, three calls matter more than the rest. The first is to the firm's retained incident-response provider, or to the insurer's preferred panel if the policy directs it. The second is to the insurer or broker, because many policies require prompt notification and some carry conditions about appointing approved specialists. The third is to the firm's professional indemnity insurer if that is a separate policy; a data breach can trigger both cyber and professional indemnity notifications.
The managing partner should also inform the firm's IT lead or outsourced provider — but as a decision-maker, not as a technician expected to solve everything alone. For firms regulated by the SRA, ICAEW or another professional body, the compliance officer should be brought in early. They will know whether the incident touches client money, undertakings or a regulatory notification duty that sits alongside the ICO's.
The 72-hour clock and the insurer's conditions
The ICO's 72-hour deadline runs from the moment the firm becomes aware of a personal data breach, not from the moment the forensic report is finished. Awareness can begin with a credible report from a client, a strange email or a locked system. The firm does not need every fact before it notifies, but it does need a reasoned view on whether the breach is likely to result in a risk to individuals' rights and freedoms.
That assessment is easier when the incident log is current and the forensic team has been appointed. A short, factual notification can be updated later. Silence, by contrast, is difficult to explain.
Insurers have their own rhythm. Some require notification within 24 hours; some require the firm to avoid engaging its own specialists until the insurer's panel is authorised. The partner handling the incident should read the notification clause aloud to the person making the call. It is a dull habit that prevents expensive arguments later.
What clients hear, and when
Rumour fills gaps faster than facts. If client data may have been exposed, the firm should prepare a holding statement before the phone starts ringing. It should say what is known, what is not known, what the firm has done so far and when clients will hear more. It should not speculate, admit liability or promise that no data was taken.
The account partner should make the first call to any client whose matter is directly affected. A generic email to the whole client base is rarely appropriate in the opening 48 hours; a targeted call from the relationship partner is. The firm's marketing or communications lead can draft the words, but the partner should deliver them. Clients remember who called, not which template was used.
The second day: one owner, one timeline
By the second morning, the incident needs a single owner. In a smaller firm this may be the managing partner; in a larger one, a nominated incident director with authority to instruct suppliers and approve spend. The owner should convene a short daily call with a fixed agenda: containment status, evidence preservation, insurer and regulatory notifications, client communications and business continuity.
Business continuity deserves its own line. Professional firms can often keep serving clients with borrowed laptops and paper files, but only if someone has decided which matters are urgent and which can wait. That decision belongs to the fee-earners, not the IT provider.
The habit that matters afterwards
The firms that emerge best from a cyber incident are not necessarily the ones with the most sophisticated technology. They are the ones that practised a sequence: contain, record, call, assess, communicate. A one-page playbook, tested once a year with a tabletop exercise, is enough to make the first 48 hours feel less like improvisation.
The ransom note is a starting gun, not a strategy. The firm's response should be calm, documented and owned at partner level — because the clock, the clients and the regulator will not wait for the system to come back online.